Firewall and VPN for business networks
Appliance, licence and commissioning: traffic control between the internet and the business, VPN for remote work and segmentation so guests cannot see business systems.
-
 Firewall / UTM appliance + licence
-
VPN for remote work and sites
-
Commissioning and rule configuration
Who it is for
For companies that have outgrown the “router from the ISP”
Network security is not a product you buy – it is a set of rules that someone has to define and maintain.
A company on the public internet
Control of what enters and leaves the network, protected admin access and logs someone actually reads.
Remote work
VPN for employees and for linking sites – business systems are not left exposed on the internet.
Guests and client devices
A separate guest network: visitors get internet, not access to your computers and printers.
Multiple sites
Offices and warehouses joined into one secure network with central rules.
Works with the environment you already use
What is in the kit
What is in the kit
Appliance and licence as specified. Rule configuration and commissioning are arranged separately, at your request.
Equipment
A firewall / UTM appliance sized by user count and traffic.
- Firewall / UTM appliance
- Licence for the security services of the manufacturer
- A spare appliance for Enterprise by agreement
Software and rules
Configuration based on how you work, at your request.
- VPN profiles for employees and sites
- Segmentation: business, guest, cameras
- Access rules and logs
Work at your request
Staged commissioning at your request, with switching windows and any outages agreed in advance.
- Staged integration into the existing network
- Rule and access testing
- IT team training and handover documentation
Firewall catalog
Models on offer – seven manufacturers
Enterprise NGFW of current generations, with a MikroTik RouterOS router when the budget calls for it and a virtual VM-Series on request – every card goes straight to inquiry, sized by traffic.
Palo Alto
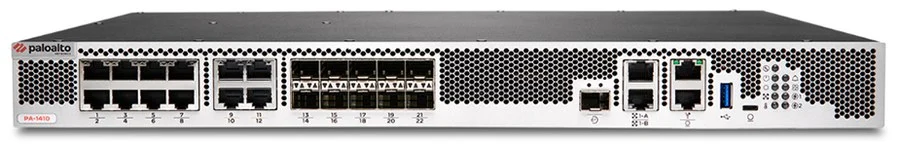
Palo Alto PA-1410
ML-powered NGFW za campus i veće filijale
- Firewall protok 8,5 Gbps (App-ID), Threat Prevention 4,5 Gbps
- IPsec VPN 4,6 Gbps, SD-WAN i Zero Trust podrška
- Centralno upravljanje politikama kroz Panoramu
Srednja klasa PA serije – najčešći izbor za centralnu lokaciju.
Palo Alto
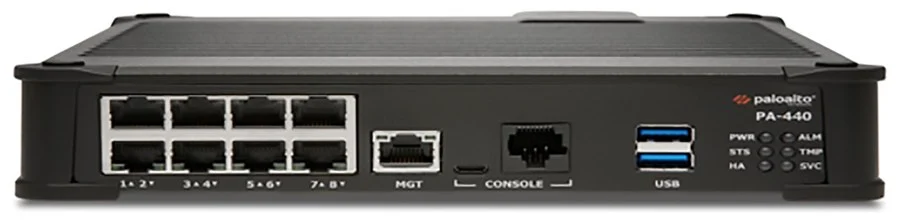
Palo Alto PA-440
Kompaktni NGFW za manje lokacije i filijale
- Firewall protok 3 Gbps, Threat Prevention do 1 Gbps
- Dimenzionisan za 50–200 korisnika u filijali
- Iste politike i upravljanje kao veći PA modeli
Desktop izvedba – bez zauzimanja rack prostora.
Fortinet
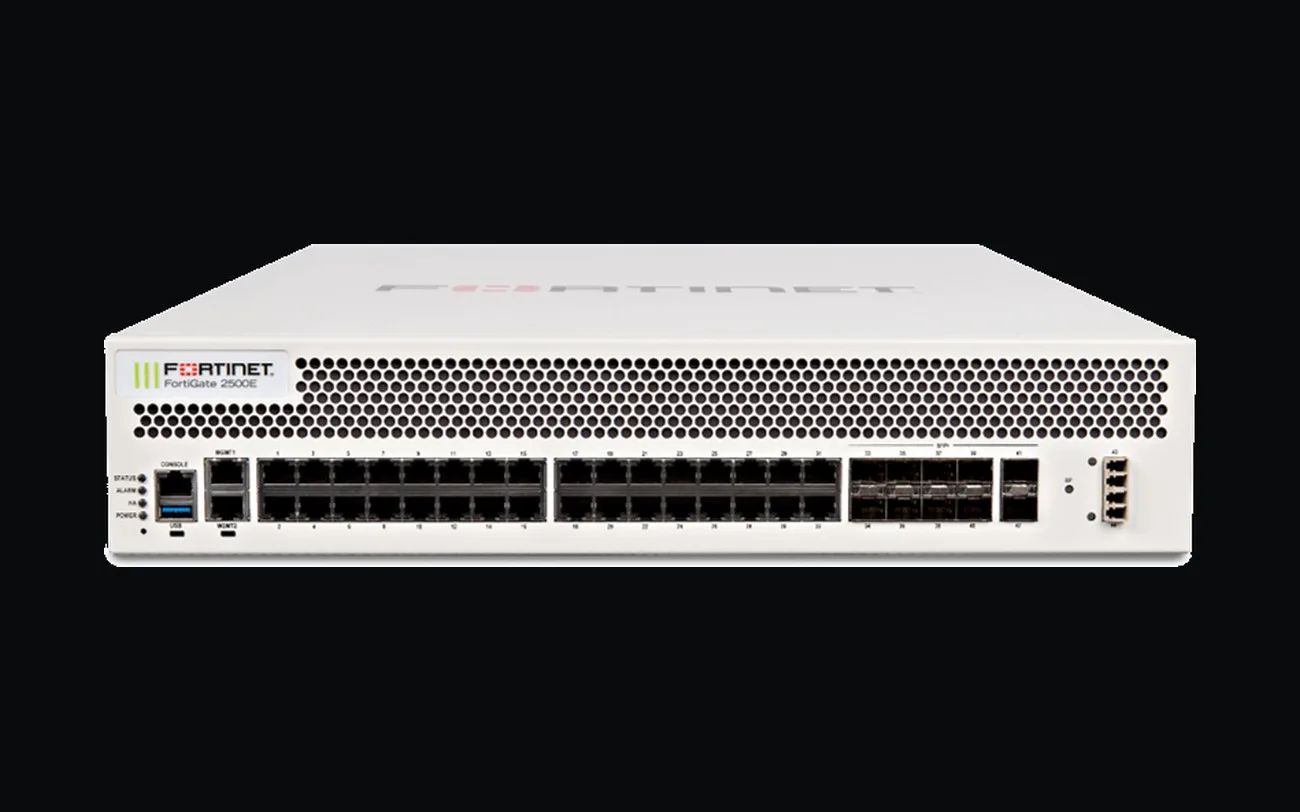
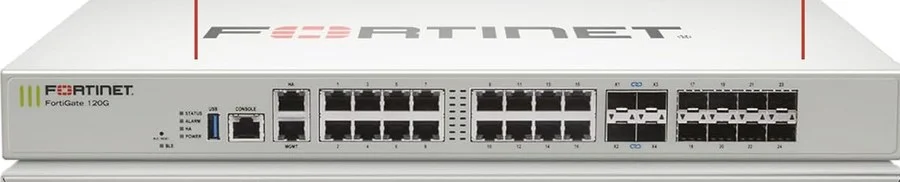
Fortinet FortiGate 120G
NGFW sa AI zaštitom za srednje firme
- Firewall protok 39 Gbps, NGFW 3,1 Gbps (enterprise mix)
- IPS 5,3 Gbps i IPsec VPN 35 Gbps
- Kombinacija GE RJ45 i GE/SFP+ portova za svaku topologiju
FortiOS i FortiGuard servisi u jednom uređaju.
Fortinet
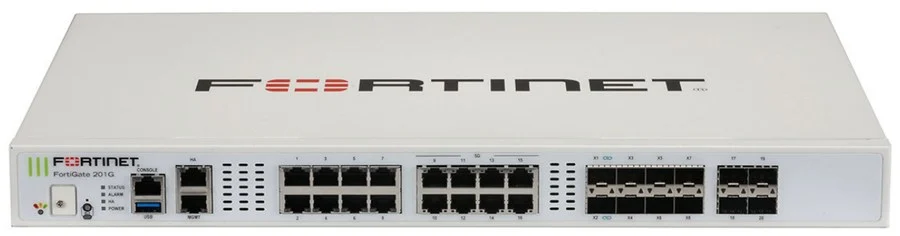
Fortinet FortiGate 201G
NGFW više klase sa redundantnim napajanjem
- Firewall protok 39 Gbps, NGFW 7 Gbps
- IPS 6,4 Gbps i Threat Protection 6 Gbps
- 11 miliona istovremenih sesija, dva napajanja
Za firme kojima treba veća garantovana preventiva.
Check Point
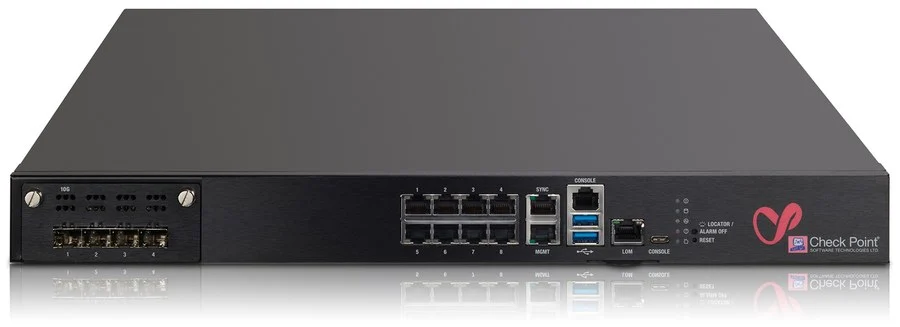
Check Point Quantum 6700
Sigurnosni gateway za data centre i veće firme
- Firewall protok do 38 Gbps (1518B)
- Threat Prevention do 19 Gbps sa svim servisima
- IPS, Anti-Bot i SandBlast Zero-Day u jednom paketu
1U gateway sa 10G uplink-ovima za zahtevna okruženja.
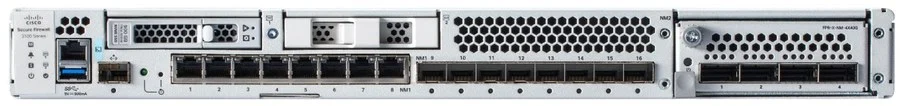
Cisco
Cisco Secure Firewall 3105
NGFW sa TLS inspekcijom za srednja preduzeća
- Firewall protok oko 10 Gbps, hardverski ubrzan VPN
- Uvid u šifrovani saobraćaj uz Cisco Talos obaveštajne podatke
- Prirodna integracija sa postojećom Cisco mrežom
Izbor za firme kojima je mreža već na Cisco opremi.
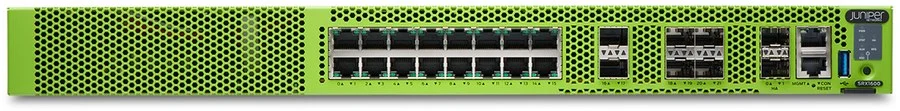
Juniper Mist
Juniper SRX1600
Next-Generation Firewall za campus edge i data centar
- Firewall protok 24 Gbps (1518B), NGFW 7,5 Gbps
- IPsec VPN 18 Gbps, do 25G interfejsi sa MACsec
- Upravljanje i analitika kroz Juniper Mist
HPE/Juniper linija – velika gustina performansi po 1U.
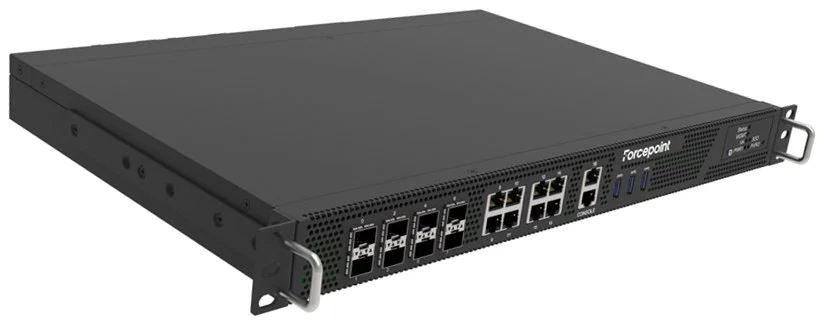
Forcepoint
Forcepoint NGFW N2210
NGFW/NGIPS za srednje i velike kancelarije
- NGFW/NGIPS protok do 13,5 Gbps
- Firewall protok do 120 Gbps (1518B UDP)
- Ugrađen SD-WAN i centralno upravljanje kroz SMC
Snažna preventiva uz povoljniji model licenci.
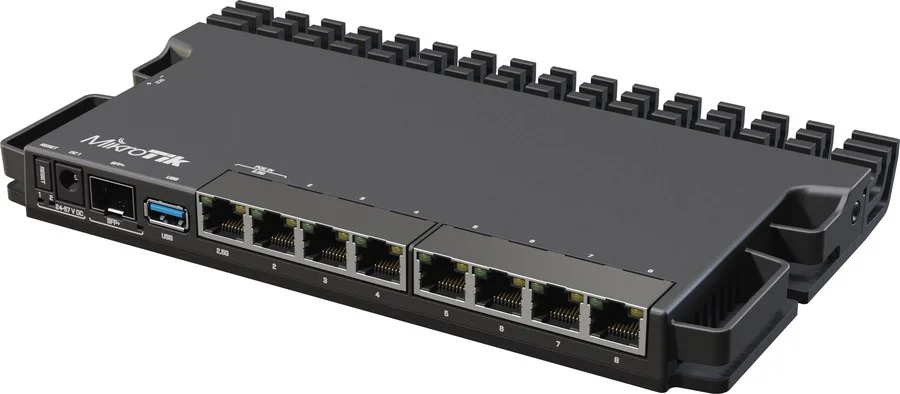
MikroTik
MikroTik RB5009UG+S+IN
Ruter-firewall za manje lokacije i filijale
- 7× Gigabit, 1× 2,5G i 1× SFP+ 10G porta, quad-core ARM 1,4 GHz
- IPsec hardversko šifrovanje (~1,3 Gbps) i WireGuard VPN
- Napajanje PoE-in, DC ili terminal, 4 komada na 1U rack polici
Kućište je ujedno i hladnjak – radi potpuno tiho.
MikroTik
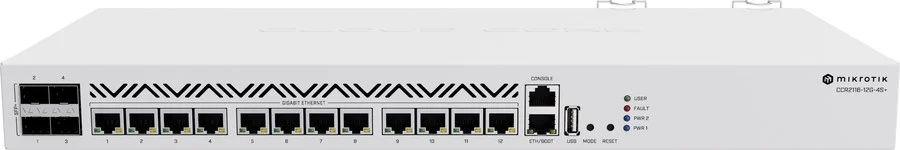
MikroTik CCR2116-12G-4S+
Centralni ruter-firewall za veće firme i više linkova
- 16-core ARM CPU – duplo veće performanse od prethodne CCR generacije
- 12× Gigabit i 4× SFP+ 10G porta, M.2 slot za proširenje
- Firewall, VPN i BGP bez licenci po korisniku (RouterOS v7)
Za 10G uplinkove ka switch core-u ili provajderu.
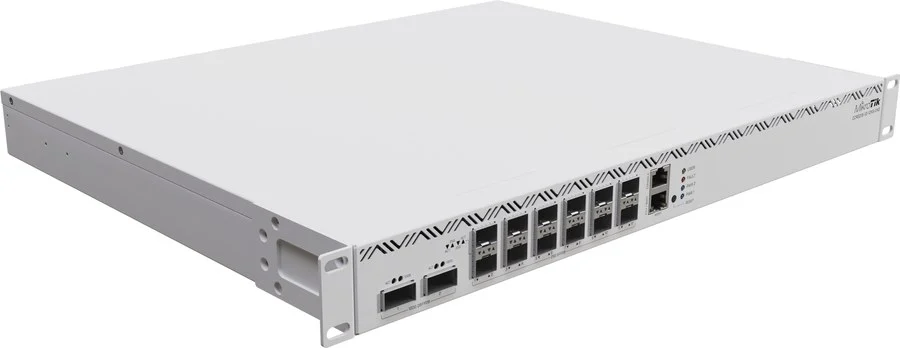
MikroTik
MikroTik CCR2216-1G-12XS-2XQ
Flagship za data centre i 25G/100G okruženja
- 16-core CPU, 16 GB RAM, 12× 25G SFP28 i 2× 100G QSFP28 porta
- Dual redundant hot-swap napajanja i 4 zamenska ventilatora
- Dva M.2 SATA slota, L3 hardware offloading za routing
Drop-in zamena za CCR1072 – isti PSU i SFP moduli.
Not sure which firewall you need?
Tell us how the network runs today – we will propose an appliance, licences and rules without over-engineering.
What is useful to tell us
- The number of users and sites the network carries
- Which applications and sites are allowed, and what is banned
- Whether a VPN or multiple internet links already exist
No models match this combination. Deselect filters or contact us.
Licences are selected by the functions you use (IPS, web filter, application control) – the specification states exactly what is included.
Capabilities
What we set up alongside the firewall
Every function is configured and commissioned together with the appliance – they are not separate projects.
Firewall
Traffic control between the internet and the company network.
VPN
Secure remote access for employees and sites.
NGFW
Application, traffic and threat control in one appliance.
IPS/IDS
Detects and blocks attacks before they do damage.
Web Filter
Blocks dangerous and unwanted sites by category.
Application Control
Controls which applications may be used, and when.
Antivirus / Anti-Malware
Stops malware already at the network level.
SD-WAN
Manages multiple internet links with automatic failover.
Network Segmentation
The network split into safe zones: business, guest, cameras.
Zero Trust Access
Access granted only to verified identities and devices.
Site-to-Site VPN
Permanent links between offices and warehouses in one network.
Remote Access VPN
Secure connections for employees working remotely or from home.
Packages
Start, Business and Enterprise – by user count
Pick a package by the number of users. The appliance and licences are listed in the specification, while rule configuration and other work are arranged separately, at your request.
Start
Up to 50 users
One location, basic protection.
- Firewall appliance sized by traffic
- VPN for remote work
- Web filter, guest network and basic rules
- Staged commissioning at your request, with switching windows and any outages agreed in advance
Most popular
Business
50–200 users
NGFW protection and more security zones.
- Everything in the Start package
- IPS/IDS, application control and anti-malware
- Segmentation by zone and site-to-site VPN
- Log monitoring and IT team training – at your request
Enterprise
200+ users / multiple sites
Redundancy and central management.
- Everything in the Business package
- A redundant appliance pair (HA cluster)
- SD-WAN and central rules for all sites
- Rule review and priority support – at your request
FAQ
Frequently asked questions
Request a kit specification
Tell us the number of users and locations – we will come back with an appliance proposal, licences and rules, with timelines.


Not sure what is looking at your network?
Send us how the network is connected today – we will propose the steps in an order that does not endanger your work.